
As soon as a website collects any personal data — an email, a contact form, cookies — it is subject to data protection regulations, the famous GDPR. Far from being a constraint reserved for large companies, compliance concerns any website, even a modest one. Good news: complying with the rules is based on simple and common-sense principles. This guide explains the essentials to make your site compliant.
What are we talking about?
The GDPR governs how personal data of internet users is collected, used, and stored: name, email, address, but also navigation data. Its basic principle is simple: respect people and their data. In concrete terms, this means being transparent about what is collected, obtaining consent when necessary, securing the data, and allowing people to exercise their rights. Nothing insurmountable for a classic website.
Essential obligations
- Transparency: clearly inform visitors about what you collect and why.
- Consent: obtain clear agreement, especially for non-essential cookies.
- Security: protect the collected data from leaks.
- People’s rights: allow access, correction, and deletion of data.
The right reflex. Apply the principle of minimization: only collect the data you really need. A form that asks for the bare minimum is easier to comply with, more reassuring for the visitor, and less risky in case of an incident. Fewer data collected, fewer problems.
Must-haves on a website
A few concrete elements make a website compliant. A clear privacy policy, explaining what you collect and how. A cookie banner allowing the visitor to accept or refuse non-essential cookies. Transparent forms, indicating the use of the requested data. And a way for people to contact you to exercise their rights. Once in place, these elements cover the essentials for a classic website.
The GDPR is about treating people’s data with respect. It means telling them what you collect, asking permission when needed, keeping it safe, and letting them control their own information. It’s not complicated if you follow these basics.
A small e-commerce site using a contact form must clearly state why it collects the email (e.g., “to answer your questions”) and only ask for the email, not the phone number. The form should also link to the privacy policy, and the site must ensure emails are stored securely, not left exposed in a public database.
Data security
Compliance also involves protecting the collected data. A secure website (HTTPS), protected access, data stored safely: all measures that prevent leaks. A personal data leak is not just a legal issue: it is a breach of trust with your visitors. Securing the data you collect is therefore both an obligation and a mark of respect for your audience.
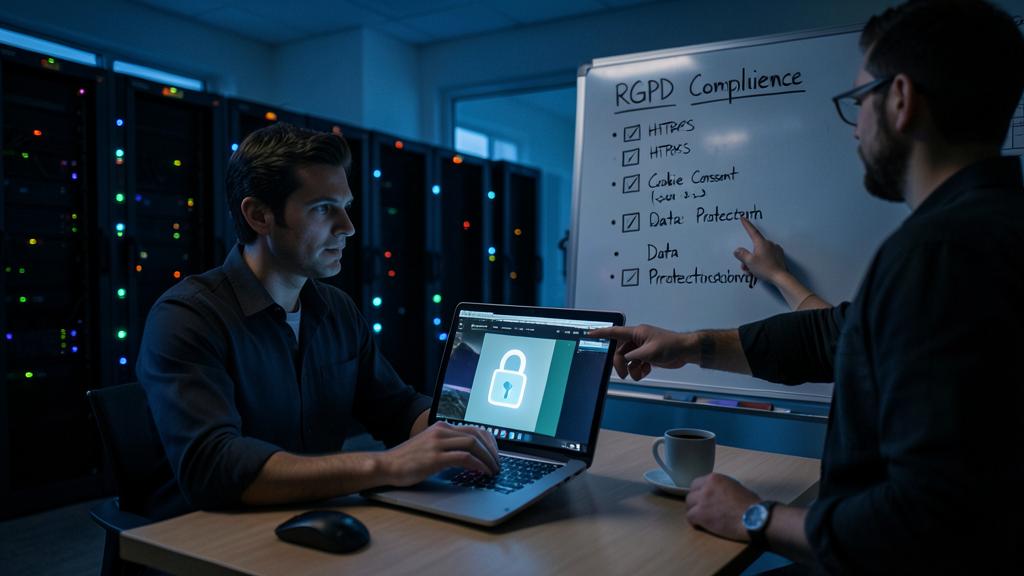
Not to be ignored. Do not consider the GDPR as « reserved for the big players »: any website collecting personal data is concerned, regardless of its size. Ignoring these obligations exposes you to sanctions, but above all betrays the trust of your visitors. Compliance is also a sign of seriousness and respect.
A quick audit: check your site in 20 minutes
Check page by page: Your forms — is each requested field necessary? Does a note indicate the use of the data? Your cookie banner — does it allow refusal as easily as acceptance? Do non-essential cookies really wait for consent? Your privacy policy — does it exist, is it up to date, accessible from every page? Your third-party tools — statistics, maps, embedded videos: which ones deposit cookies or transfer data, and is this covered by your information? Your emails — do your sends include a functional unsubscribe option? Note the discrepancies, correct them by priority: compliance is an ongoing improvement project, not an exam to pass on the first try.
Frequently asked questions
Is my small website really concerned?
Yes, as soon as it collects personal data (form, email, cookies). The obligations adapt to your activity, but the basic principles apply to everyone.
Do I need a lawyer?
Not for the essentials: the basics (privacy policy, cookies, minimization, security) are accessible. For complex processing, support may be useful.
Are statistics tools compatible with the GDPR?
Some audience measurement tools, correctly configured or designed for privacy, can work without prior consent; others require it. Check your tool’s position and adapt your banner and policy accordingly.
What to remember
The GDPR is not a constraint reserved for large companies: any website collecting personal data is concerned. Compliance is based on common-sense principles: transparency about what is collected, consent for cookies, data security, respect for people’s rights. In practice, a clear privacy policy, a cookie banner, transparent forms, and a secure website cover the essentials. Apply minimization — only collect what is necessary — and you will combine compliance, security, and the trust of your visitors.
Need to make your site compliant?
Leave a Reply
You must be logged in to post a comment.